Anthropic publishes AI formal verification research: security assurances still depend on explicit assumptions
Anthropic and Theorem published research on using Claude to assist software formal verification, proving program safety properties under specific RISC-V and Linux model assumptions. The research does not establish that all programs, platforms or vulnerabilities are safe.
Source Facts
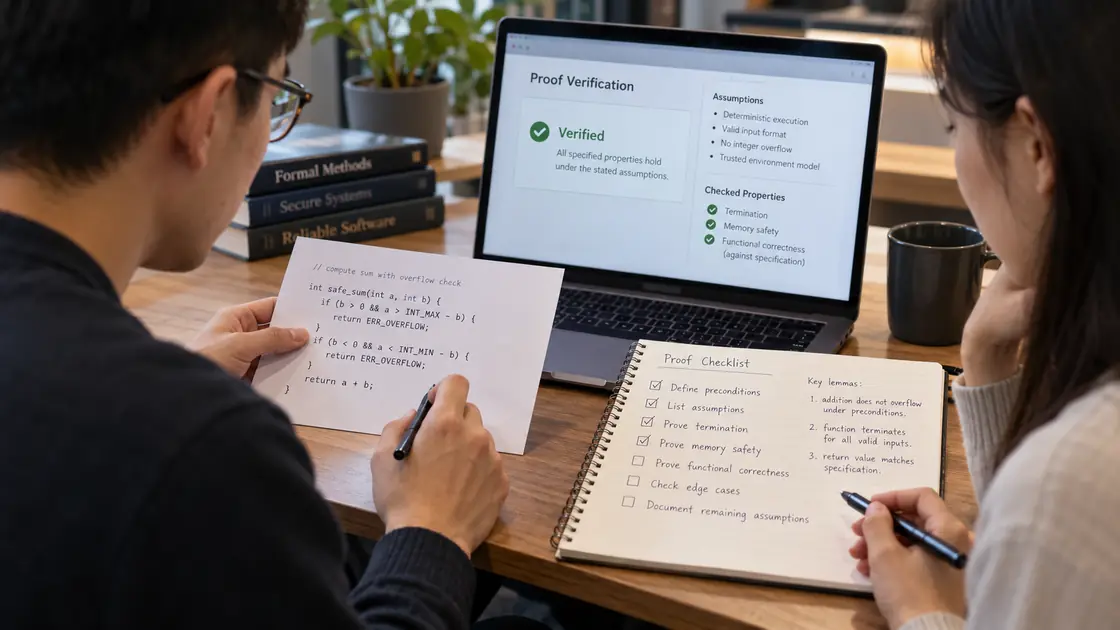
On 22 October, Anthropic introduced formal verification research with Theorem, using Claude to build proofs for several open-source libraries and check properties such as memory safety and assertions under specified execution conditions. Some proofs and semantic models have been made public.
The research guarantees have a specified scope, including single-threaded execution, a fixed memory budget, RISC-V and modelled Linux behaviour. The article notes that complete, explicit specifications for complex applications remain a major challenge in scaling verification.
When assessing an AI-written proof, first examine which properties it covers and which assumptions it depends on before deciding whether it applies to your deployment.
Original sources
LLMs are making formal software verification feasible at a much larger scale
Sources checked: 2026-10-26 · Prepared with SI agent assistance; articles have not been individually reviewed by a person.
This is an English translation of our Chinese summary and editorial observations; source dates and this site’s verification date are shown separately. If an original advisory changes, refer to the source.
KEEP READING
Recommended reading
 Illustration
LiteLLM explains package compromise: exposed keys must be revoked to complete the response
 Illustration
OpenAI details training environment isolation improvements, using offline operation and continuous red teaming to constrain agents
 Illustration