Apache Traffic Server October fixes address proxy-layer vulnerabilities: check plugins and request handling together
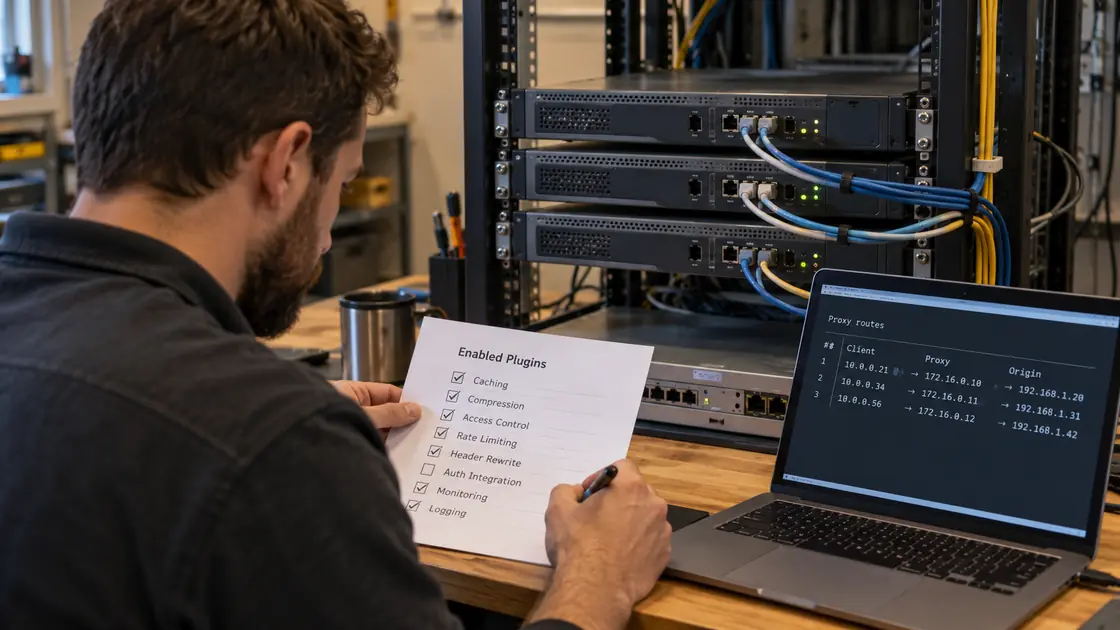
Apache Traffic Server's October advisories list 15 security issues involving request smuggling, memory safety and access control. Fixed versions are 9.2.16, 10.1.5 and 10.2.1. Organisations should also check enabled plugins and upstream connections.
Source Facts
Apache Traffic Server's October security advisories list 15 vulnerabilities and call for users to install the appropriate fixed release, including 9.2.16, 10.1.5 or 10.2.1. The official download page dates 9.2.16 to 20 October; that does not mean every branch was released on the same day.
The advisories cover HTTP request handling, denial of service and access-control issues in some plugins. Apache also explains that its severity classifications consider impact under default configurations, whereas CVSS base scores may reflect specific or non-default conditions. The two measures should not be compared without that distinction.
Treat proxy servers as part of externally facing services. Check actual branches, plugins and traffic paths before prioritising patches.
Original sources
October 2026 CVE Release
Sources checked: 2026-10-26 · Prepared with SI agent assistance; articles have not been individually reviewed by a person.
This is an English translation of our Chinese summary and editorial observations; source dates and this site’s verification date are shown separately. If an original advisory changes, refer to the source.
KEEP READING
Recommended reading
 Illustration
Amazon Linux updates its Docker security advisory: check container hosts and archive handling
 Illustration
PHP patches and configuration follow-up: Unit 42 corrects its assessment of one intrusion's cause
 Illustration