NGINX October fixes cover HTTP/3 and TLS: check modules and configuration first
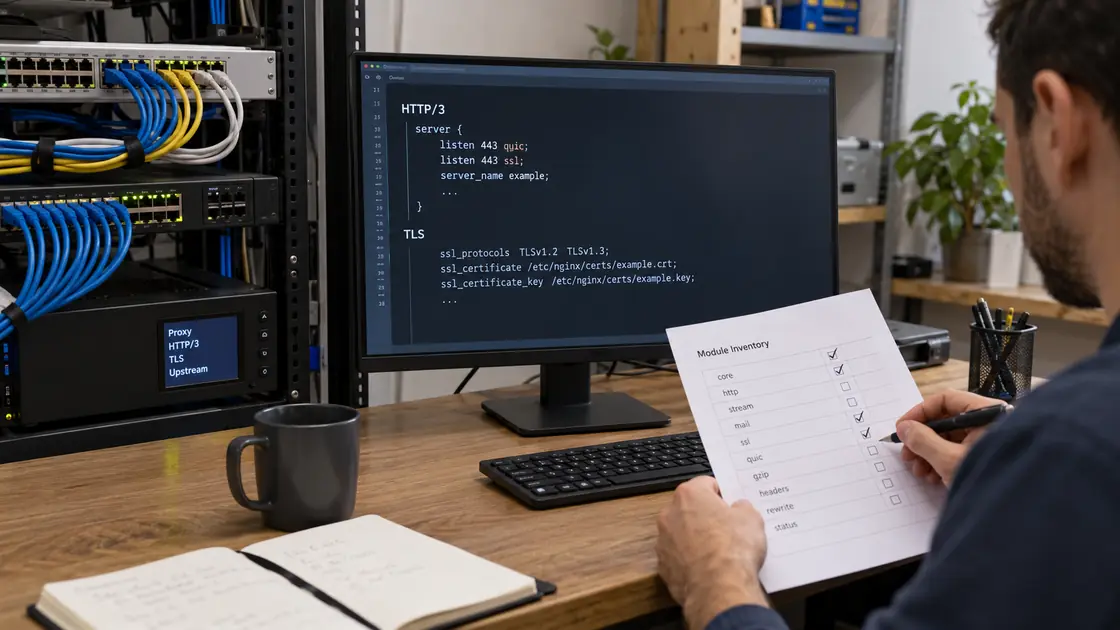
NGINX releases stable version 1.30.6 and mainline version 1.31.7, fixing several issues dependent on particular modules or configurations, including HTTP/3 request handling, TLS sessions and memory safety. Include hosting providers and reverse proxy appliances in the inventory.
Source Facts
NGINX's annual news page lists 1.30.6 and 1.31.7, released on 14 October for the stable and mainline branches respectively. Listed fixes involve alias and rewrite, string operations containing variables, HTTP/3, TLS session ticket key rotation, and the combination of SSI with asynchronous I/O.
These issues include buffer overflows, request-content injection, session forgery and use-after-free. Determine exposure to each vulnerability by comparing the advisory with enabled modules. Seeing the NGINX name alone does not mean every issue can be triggered.
Reverse proxy modules and settings matter as much as versions. Hosted websites should confirm patching with their provider, not just update the content management system.
Original sources
nginx news: 2026 — 2026-10-14 releases
Sources checked: 2026-10-26 · Prepared with SI agent assistance; articles have not been individually reviewed by a person.
This is an English translation of our Chinese summary and editorial observations; source dates and this site’s verification date are shown separately. If an original advisory changes, refer to the source.
KEEP READING
Recommended reading
 Illustration
Amazon Linux updates its Docker security advisory: check container hosts and archive handling
 Illustration
PHP patches and configuration follow-up: Unit 42 corrects its assessment of one intrusion's cause
 Illustration