NSA publishes MCP security design considerations: review tool connections together with trust boundaries
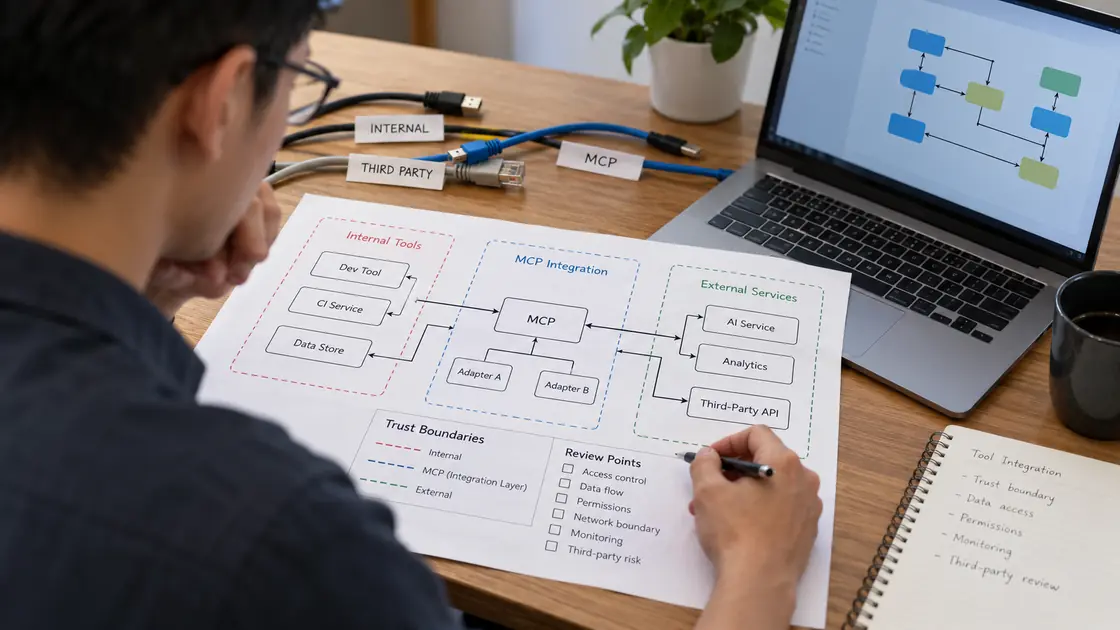
NSA's AI Security Center published MCP design considerations, reminding organisations to consider dynamic tool calls, shared context and implicit trust alongside authentication, authorisation and input validation. The guidance concerns deployment risks; it does not mean all MCP services share one vulnerability.
Source Facts
NSA published a cybersecurity information sheet on MCP on 20 May, examining design, implementation and operational risks when AI systems connect services into workflows, including serialisation, trust boundaries and agent misuse.
The guidance says conventional authentication, authorisation and input validation remain necessary but cannot alone address systemic risks from dynamic tools and context sharing. Organisations should examine the entire agent environment rather than patching a single interface.
Before introducing MCP, map which services trust one another, what each can read or write, and which tools pass on external content.
Original sources
NSA Releases Security Design Considerations for AI-Driven Automation Leveraging the Model Context Protocol
Sources checked: 2026-10-26 · Prepared with SI agent assistance; articles have not been individually reviewed by a person.
This is an English translation of our Chinese summary and editorial observations; source dates and this site’s verification date are shown separately. If an original advisory changes, refer to the source.
KEEP READING
Recommended reading
 Illustration
LiteLLM explains package compromise: exposed keys must be revoked to complete the response
 Illustration
SOCRadar examines SI agent-assisted extortion: human approval remains part of the intrusion process
 Illustration